Security Watchtower
Advisories and incident analysis.
Page 4 of 61
CVE Analysis Center
BeyondTrust Remote Support CVE-2026-102764: Zero-Day Exploited Since August, Now in CISA KEV
CVE Analysis Center
Cisco Secure Email Gateway CVE-2026-76519: Actively Exploited File Write Flaw Added to CISA KEV
Active Exploitation Alert
Ivanti Connect Secure Zero-Day Exploit Chain Enables Root-Level RCE and Credential Theft on Fully Patched VPN Appliances
Cybersecurity Incident Analysis
TFG London Cyberattack Disrupts IT Systems and Online Services at Phase Eight, Hobbs, and Whistles Brands – October 2026 Incident Analysis
Cybersecurity Incident Analysis
Insider Espionage at OpenAI: Cyber-Physical Attack Using Hidden Audio Recording Devices Highlights AI Sector Security Risks
CVE Analysis Center
Critical CVE-2026-89111 SSRF Vulnerability in SAP Cloud SDK for Python Threatens SAP BTP OAuth2 Security
CVE Analysis Center
AhsayCBS Backup Console Under Active Exploitation: CVE-2026-105133/105134 Chain Leads From Auth Bypass to RCE, and 10.3.4.0 Does Not Close It
Cybersecurity Incident Analysis
Ledger Hardware Wallet Supply Chain Attack: $90M Cryptocurrency Theft Linked to CryptoBilis Reseller in Southeast Asia
Blog posts
From Dependency to Resilience: Redefining Third-Party Risk Across Industries
Cybersecurity Incident Analysis
Daiichi Kosho Supply Chain Data Breach: Nippon Columbia Malware Incident Exposes 8.6 Million Karaoke Customer Records
CVE Analysis Center
SonicWall SMA1000 CVE-2026-102255: Third Pre-Auth SSRF of 2026 Makes "Patched in September" Out of Date
Cybersecurity Incident Analysis
Scala Communications i-ask FAQ platform breach (Daiwa / Citizen / Sompo)
Cybersecurity Incident Analysis
Oracle Health (Cerner) 2026 Data Breach Exposes Nearly 20 Million Patient Records Across 80 U.S. Hospitals
Cybersecurity Incident Analysis
ASOS Data Breach 2026: Cybersecurity Incident Analysis of Third-Party Compromise and Social Engineering Attack
Active Exploitation Alert
Zimbra Collaboration CVE-2026-73570 — Unauthenticated OS Command Injection via Crafted SMTP (KEV)
Cybersecurity Incident Analysis
Ernst & Young 2026 Data Breach Analysis: Third-Party IT Support Platform Compromise Exposes Sensitive Client Information
Cybersecurity Incident Analysis
Arizona Supreme Court Cyberattack Exposes 30 Years of Court Debtor and Foster Care Data, Impacting Over 1.3 Million Individuals
Technology
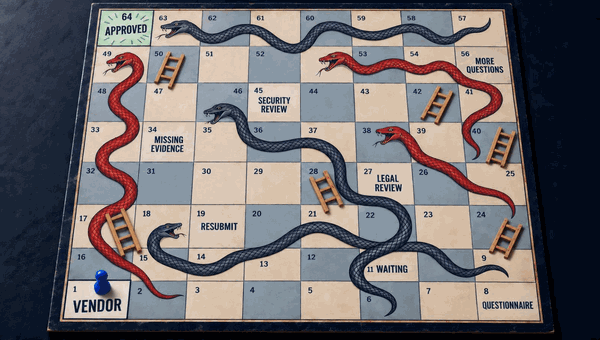
Why Vendor Risk Moves Faster When Everyone Has the Full Picture
Email Security
Nikkei Inc. Discloses Microsoft 365 and Google Workspace Email Account Breaches Used for Phishing and Data Exposure
Flydubai_Everest_Breach_Claim_Advisory_Oct_2026
Cybersecurity Incident Analysis
FBI Data Breach Analysis: ShinyHunters Exploit Unpatched Oracle PeopleSoft CVE-2026-35273 Due to Third-Party Patch Failure
CVE Analysis Center
Denmark CPR Registry: Lawful Third-Party Lookup Access Abused, About 8.8 Million People's Names, Addresses and CPR Numbers Accessed
CVE Analysis Center
CVE-2026-96940: Critical Microsoft Exchange Server Vulnerability Enables Privilege Escalation and Unauthorized Mailbox Access
CVE Analysis Center